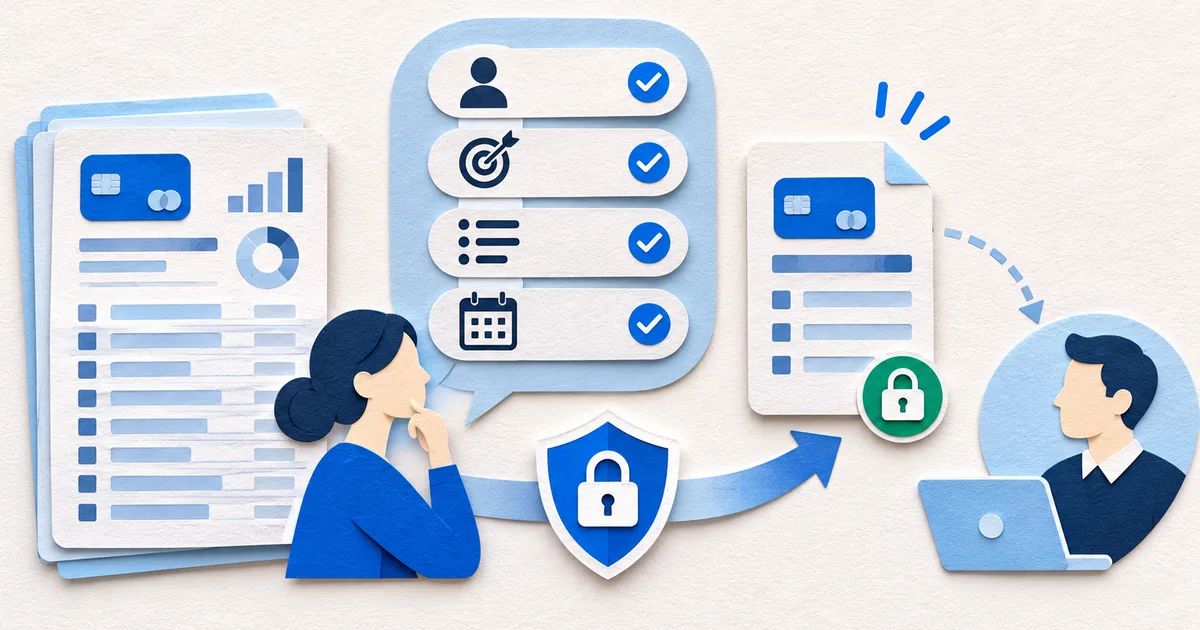
How to Share a Credit Card Statement Securely
Secure sharing begins before encryption: verify the requester, send the smallest useful record, and control who can open or keep it.
Transfer lab: design the smallest useful disclosure
Maintain a disclosure record with request authority, purpose, file version, recipient, channel, send time, expiry, download permissions, password path, confirmation, and revocation time. Ask the recipient to confirm the cycle and version without repeating sensitive figures in an insecure message. Revoke an unused link rather than leaving it active and record any delivery failure or replacement.
End the lifecycle deliberately. Establish the recipient's retention need, remove temporary exports and drafts, clear scanner or mobile copies, and preserve only the controlled original and required disclosure record. If a link, version, or recipient was wrong, act immediately and retain incident facts for the responsible party's review. Do not assume that a requested deletion erased backups or prior downloads.
If several people inside one organization need the document, ask for the minimum named access group rather than forwarding separate attachments. Use portal permissions that can be reviewed and revoked, and avoid shared credentials. Keep download permission off when viewing alone meets the purpose. The disclosure record should identify the organization and the people or role authorized at the time.
Reassess recurring requests rather than assuming the first authorization lasts forever. The needed cycles, fields, recipient, legal basis, and retention can change. A new request should confirm current scope and contact details and should not reuse an old link or password. This prevents a convenient routine from becoming permanent access to an expanding card history.
Use a stop rule for suspicious urgency. A request that resists independent verification, demands an unnecessary full history, changes its destination, or insists on bypassing an established portal should pause delivery. Confirm with the organization through a known route and involve the relevant account owner or privacy contact. Meeting a deadline is not a reason to ignore a mismatch between requested information, recipient authority, and the stated purpose.
For physical delivery, apply the same reasoning: verify address and recipient, use tracked or controlled handling where appropriate, avoid transparent packaging, and record receipt. A printed statement cannot be revoked remotely, so minimize it carefully and confirm the recipient's disposal or retention expectation before sending rather than treating paper as automatically safer than digital transfer.
If the recipient does not need every field, prepare the copy with the credit card statement redaction method and inspect the exported file rather than trusting a visual overlay.
For analysis on this site, confirm the temporary-file controls in the CreditCard-Statement.com privacy policy before sending any authorized statement.
For an authorized document that needs analysis rather than delivery, use the temporary credit card statement workspace and review its expiry and storage choices first.